After the last three weeks of having back to back discovery calls with AI transformation experts around the world, I'm noticing a disturbing commonality that isn't isolated by geolocation or industry vertical. And I think it warrants a larger discussion.
CIOs, TAKE NOTE! The observation in question? GHOST AI. Let's unpack.
Backdrop
For context, we're getting ready to release our enterprise product, so I've spent the last three weeks interviewing AI transformation consultants as prospective educators, brand advocates and distribution partners. The reception's been better than I hoped, genuine excitement, people get what we're building. But as soon as we get onto core enterprise pain points, the same worry surfaces every single time. Currently, in most companies, staff are feeding client data, contracts & source code into AI tools nobody approved, and leadership has no idea it's happening.
Ghost AI
If you haven't heard the term, here's the short version. Ghost AI is what happens when your people are already using AI on their own personal plans, without the company knowing or approving any of it. No visibility, no policy, no record. Just employees quietly getting their work done faster.
My observation is that most companies navigating AI adoption have no grasp of it at all. No idea what's going into these tools. It could be company secrets. It could be commercial IP. It could be client data. Worse, they've got no idea whether the data transfer and compute happening inside those self made workflows is breaching a regulatory framework, a compliance obligation, or the terms of a commercial contract they've already signed. This is a massive gap in commercial literacy around AI, and a lag in enterprises proactively planning their agentic transformation. That failure to plan has meant decision makers have unintentionally passed that responsibility onto their workers, and it's creating a problem no one has realised yet.
The employee isn't doing anything malicious. They're not trying to leak anything. They just want to be more productive and the tool in front of them makes that possible. Their intent is good but the exposure they're creating is enormous.
Where the governance gap actually is
With enterprises, businesses and corporations rushing to adopt AI, their upstream SaaS vendors are in the same race to make their tools interoperable with AI. Connectors, plugins, MCP, etc. That adoption pivot is moving fast. SaaS vendors' ability to adapt and adopt rapidly to market demand is no surprise. But the issue is, there was no thought at all given to governance. And what I'm seeing is that it hasn't carried through as part of that interoperability play.
I think about what I can actually control as an admin. Take our Google Workspace for example. I can force two-factor authentication on every employee, nobody gets a choice. I can decide which third-party apps are even allowed to connect to our data, right down to the specific permissions they get. There are some levels of real controll, granted. But there's a whole side door none of these controls can manage.
I can't set a rule that says every piece of company data heading into an LLM has to be approved first. Those app-level controls only cover the tools that come through the front door with an account and permissions. They do nothing about someone sitting on their personal ChatGPT tab, on their own plan, pasting a client contract in to tidy it up. No connection to govern, no scope to limit, no log. Copy, paste, gone.
Then there's the fragmentation issue. That copy-paste path is its own problem. Even where a SaaS product does give admins some control, it's not consistent across every tool a company runs, so people just route around it the oldest way there is. They lift the thing out of the governed system and drop it into the ungoverned one.
Samsung found this out the hard way. Their engineers pasted proprietary source code into ChatGPT to debug it. Internal meeting notes went in too. That was early 2023, and nobody has ever been able to pull that data back.
The reaction was the one everyone reaches for. Ban the tool. Lock it down. Distribute the "no no" memo company wide.
The issue is, a memo doesn't fix this. Enforcement by policy is flimsy. This needs to be addressed and enforced at a codebase level. This isn't isolated to the Samsung situation, as the numbers prove.
IBM's 2025 Cost of a Data Breach report found one in five breaches now involves shadow AI, and those breaches cost an extra $670,000. 97% of the organisations hit had no real controls on what AI could reach. 63% had no AI governance policy at all.
Cyberhaven tracked 1.6 million workers and found roughly a third of the corporate data people paste into AI tools is now sensitive, up from a tenth two years ago and still climbing.
In Gartner's 2025 survey of security leaders, 69% suspected or had already caught staff using forbidden public AI tools.
40% of enterprises will face a shadow-AI breach by 2030.
The key takeaway here is that this is happening inside most companies right now, whether the board knows it or not.
The Blockbuster moment
Here's why I think a larger discussion on this subject matter needs to be had. Boards are only just waking up to the applications of AI in a commercial setting. A lot of them are realising an uncomfortable truth. Their competitors didn't drag the adoption anchor. They put a real AI transformation strategy in place twelve months ago, they've been using it properly across the whole business, and that's exactly why they're winning now. Beating them on sales. On marketing. On advertising. On finance management. On vertical intel. Beating them on literally every benchmark that departments orient their KPIs around. Why? They adopted AI early, tested, refined and promoted workflows & got ahead where others lagged.
These early adopters have built a MOAT from a year of using AI in a cohesive, cooperative way across the entire workspace, while everyone else was still arguing about whether to allow ChatGPT.
I like to call this the AI Blockbuster moment. Companies that fail to adopt early don't get a warning. They just lose, quarter after quarter, to the ones that did.
What a governed business actually looks like
I think we've nailed governance pretty well within our own product. It was a key pain point for us early on. Working out how to transform an organisation from a static entity, with siloed context and data, into a living, AI-powered organism that truly empowers teams and workflows forced us to map exactly where context needs to be available, where it needs capping or restrictions, and where it doesn't belong at all.
BlueNexus lets an organisation become a kind of digital life form.
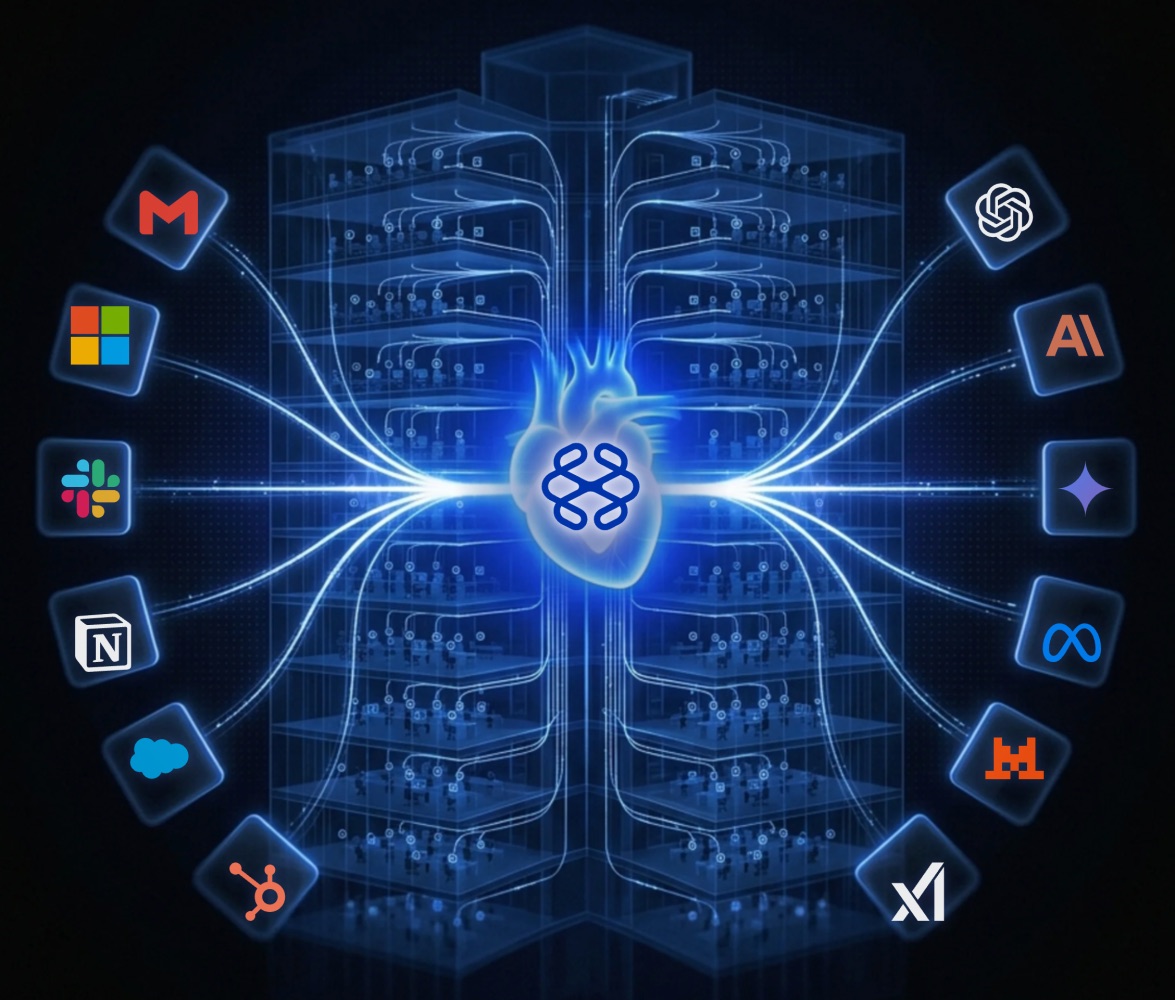
The model is the brain. The business is the body. And BlueNexus, the harness, is the heart. Our job is to orchestrate the metaphorical pumping of blood (workflow context) throughout the whole body, turning the company's own workflows into a life form in themselves.
Currently, with the incumbent tools available, that blood doesn't flow. Everything's fragmented. Even in companies with a proper AI adoption policy you've got people running individual agents in siloed little environments, and the legacy harnesses underneath them were never built to let context move between teams.
An example
Say a marketing department is putting together something for investors, and to do it properly they need numbers from sales and accounting. In today's agentic enterprise setup there's no clean way for those teams to work in the same flow with the right access. Marketing doesn't need to see the entire profit and loss from last quarter. But they do need last quarter's sales figures. A correctly governed environment would give marketing exactly the data they need and nothing they don't, and let Finance, Sales and Marketing collaborate inside one workflow, their agents powering the data rails and compute. This is the pain point we're solving.
Our goal is to enable businesses to transform from a pile of disconnected tools into a living, context-rich, governed ecosystem. A nexus. Something closer to mycelium than an org chart. Living, breathing, context moving where it needs to go, and only where it's allowed to.
None of this works by banning things. Ban the tool and the shadow just moves somewhere you can't see it. The only thing that actually works is giving people a sanctioned place to do the exact work they're already doing on the side, with the guardrails built in instead of bolted on. Know who can access what, what's sensitive, what's current, and keep a record of what the AI actually touched. Do that, and a CIO can finally say yes to AI and still sleep at night.
My closing question to CIOs, or anyone wrangling with internal AI policy right now, is this: if someone on your team pasted a client contract into ChatGPT this morning, would you even know? If the answer's no, my DMs are open.
Let's assess how BlueNexus can be your enterprise partner of choice for your corporate AI adoption plan.
Originally published on LinkedIn.